5 Years ExperienceAWS Security SpecialtyAWS DevOps ProfessionalTerraform CertifiedCloud Engineer @ PlurilogicAWS + AzureDevSecOpsSOC 2 · HIPAA70% Cost ReductionBased in Canada

TARANDEEP SINGH · DEVOPS · CLOUD · CLOUD SECURITY · TORONTO

Hi, I'm
Taran.

AWS Certified Security – SpecialtyAWS Certified DevOps Engineer – ProfessionalAWS Certified Developer – AssociateHashiCorp Certified: Terraform Associate

I build cloud infrastructure that is secure by default and reliable in production.

I have five years of experience on AWS and Azure, working mainly with Terraform and Kubernetes. I enjoy automating manual work, reducing cloud costs, and closing security gaps before they become problems.

01

Experience

5 yrs

Cloud & DevOps

70%

Cost Reduction

90%

Faster Provisioning

SOC 2

& HIPAA Controls

CLOUD ENGINEER

Apr 2026 – Present

  • Built AWS infrastructure for an internal AI knowledge assistant using Bedrock, Terraform, and GitHub Actions
  • Run EKS for 35+ microservices across 15+ tenants, with autoscaling, RBAC, Argo CD, and zero-downtime deploys
  • Built Azure infrastructure for a federated ML platform used by 200+ institutions, using Azure ML and NVIDIA FLARE
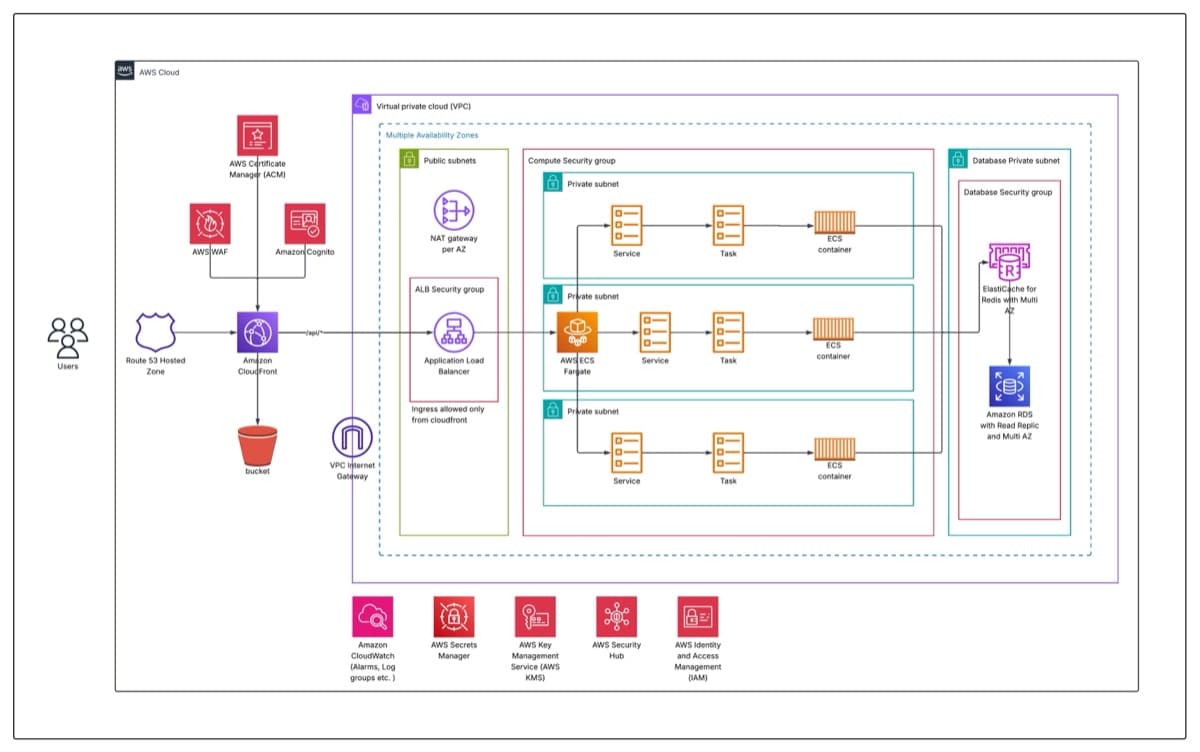
  • Set up production security controls: least-privilege IAM, AWS WAF, encryption, and Secrets Manager
RESEARCH ASSISTANT

Jan 2026 – Mar 2026

  • Built and deployed an AI writing tool that guides students with ADHD step by step through research and academic writing
  • Deployed with Docker and delivered to students through Moodle

GRADUATE TEACHING ASSISTANT

Sep 2025 – Dec 2025

  • Built a web app for assignment submissions with automated peer assessment, saving instructors 10 hours a week across 90 students
  • Supervised 90 students in virtual and in-person classes, and helped instructors plan and deliver lessons

SENIOR DEVOPS ENGINEER

Aug 2024 – Jan 2025

  • Migrated Windows Server (AD, file, print) with no downtime for thousands of users in 80+ countries
  • Moved separate tenant deployments onto a shared multi-tenant AWS platform, cutting infrastructure cost by about 70%
  • Managed 257 production AWS resources, including availability, IAM governance, and disaster recovery

DEVOPS ENGINEER

Sept 2022 – July 2024

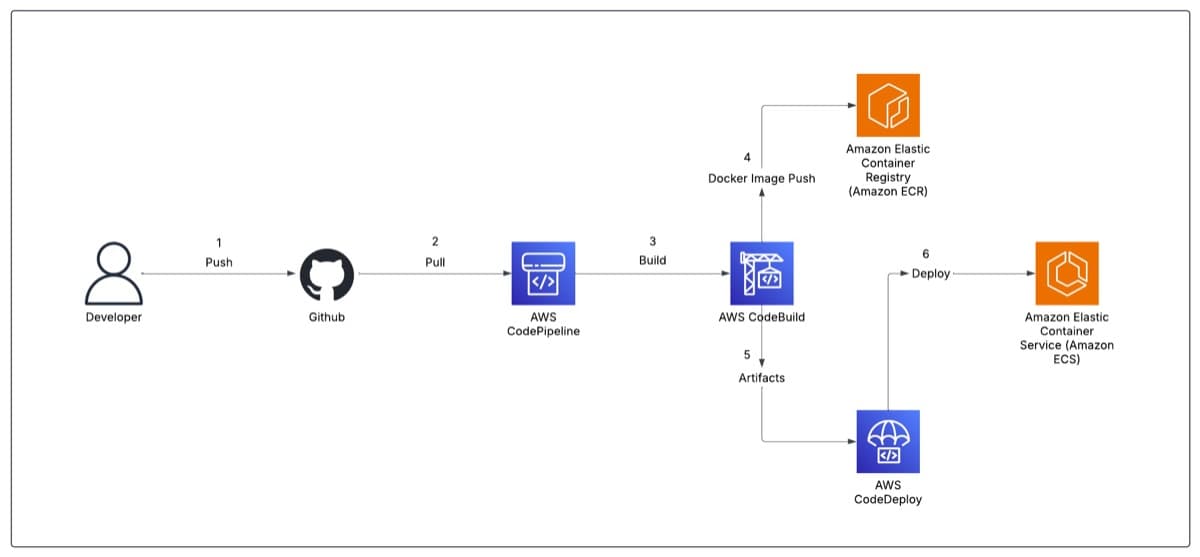
  • Built CI/CD for 8+ applications with Jenkins, CodePipeline, Azure DevOps, and GitHub Actions, with Snyk and SonarQube checks in every pipeline
  • Supported SOC 2 and HIPAA compliance with Security Hub, Config, and Inspector
  • Cut cloud costs by about 40% by moving to Graviton and shutting down non-production environments outside working hours

JUNIOR DEVOPS ENGINEER

Mar 2021 – Aug 2022

  • Wrote reusable Terraform modules and Python and Bash scripts to standardize deployments
  • Cut deployment time by 40% by tuning and debugging pipelines

02

Skills

CLOUD

AWS
EC2, EKS, ECS/Fargate, Lambda, VPC, RDS, S3, CloudFront, Route 53, API Gateway, SQS/SNS
Azure
AKS, App Service, VNet, Storage, APIM, Azure DevOps
AI Infrastructure
AWS Bedrock, SageMaker, Azure ML, NVIDIA FLARE
Systems & Data
Linux, Windows Server, DNS, TCP/IP, Postgres, MySQL, Redis

DEVOPS

IaC & Containers
Terraform, Docker, Kubernetes, Helm
CI/CD
GitHub Actions, Jenkins, Argo CD, GitLab CI, CodePipeline, Azure DevOps
Observability
Prometheus, Grafana, CloudWatch, ELK, Splunk, Datadog
Automation
Python, Bash, YAML

CLOUD SECURITY

Identity & Access
Least-privilege IAM, Kubernetes RBAC, Azure RBAC
Data & Network Protection
AWS WAF, encryption at rest and in transit, Secrets Manager, Key Vault, security groups
Posture & Compliance
Security Hub, AWS Config, Inspector, SOC 2, HIPAA
DevSecOps
Snyk (SCA), SonarQube (SAST), pipeline security gates

03

Projects

Personal

Production Kubernetes Platform at Home

The platform this website runs on: a k3s cluster in my home with GitOps delivery, zero-trust ingress, live observability, self-hosted analytics, and a cloud fallback.

Serves this site live; commit to production in minutes, full rebuild from git with one command

Security
Zero open ports through Cloudflare Tunnel. Prometheus, Argo CD and analytics are private behind NetworkPolicies, RBAC is least-privilege, and secrets live in git only as SealedSecrets.
Built with
k3sArgo CDHelmGitHub ActionsCloudflare TunnelTraefikPrometheusFastAPISealed Secrets
More details
  • Delivery: CI tests and builds each image with an SBOM and build provenance, pushes it to GHCR, and pins the tag in a GitOps repo that Argo CD rolls out as app-of-apps.
  • Observability: an SRE dashboard on this site shows golden signals, saturation, deployments and visitors live, through a backend-for-frontend so nothing internal is exposed.
  • Resilience: disaster recovery is one bootstrap script plus two backed-up keys, and Vercel keeps a fallback copy of the same commit.
Personal

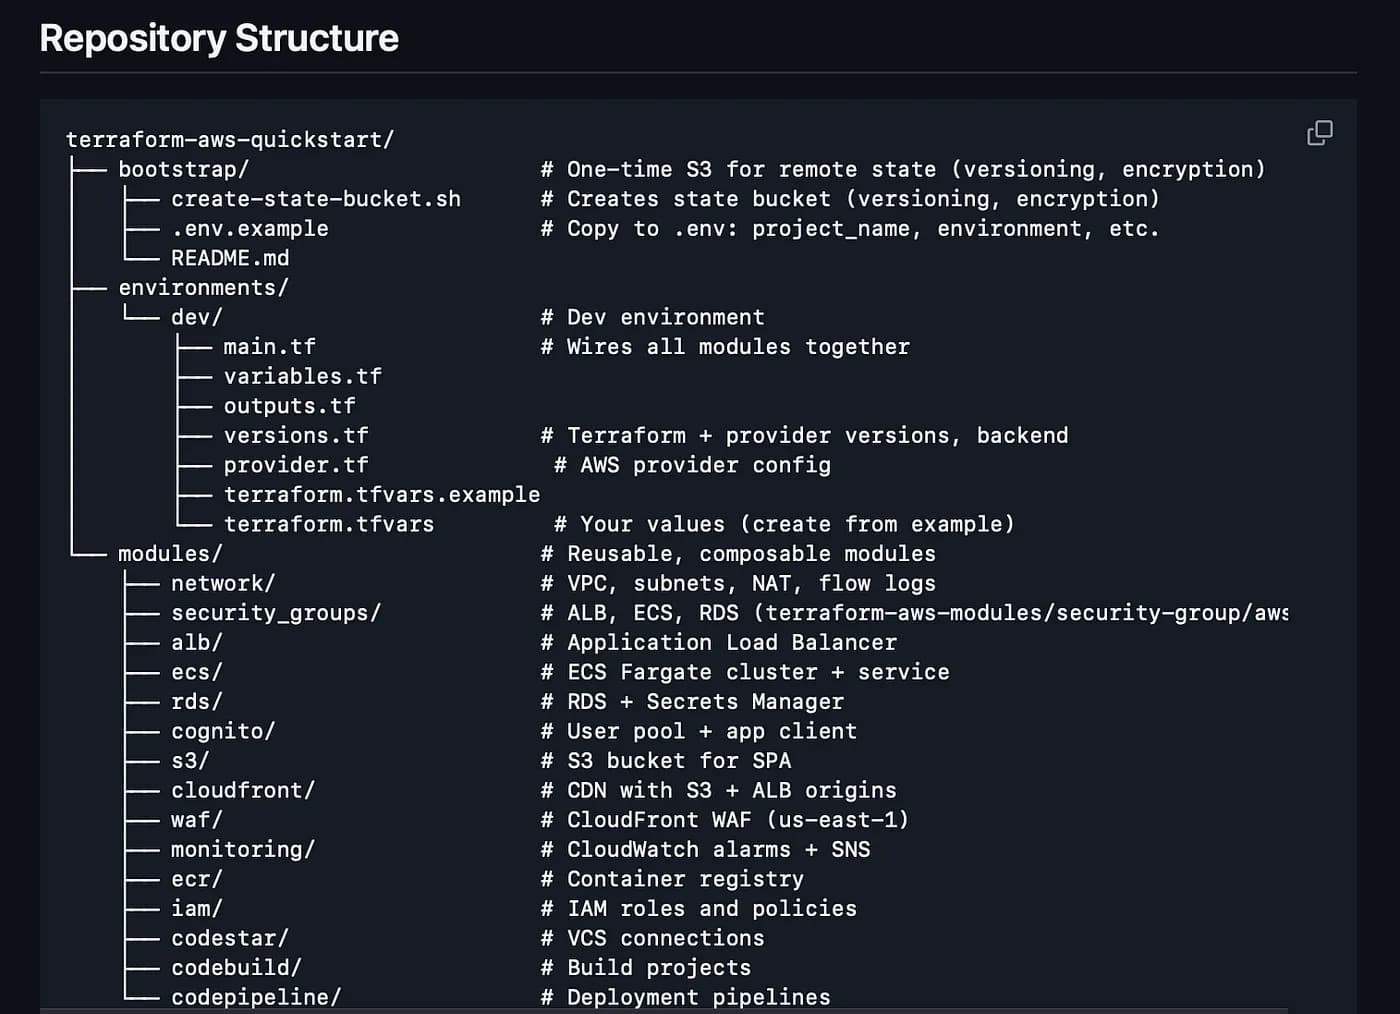
Terraform AWS Security Baseline

A Terraform module that switches on AWS's core security services in a new account and alerts on serious findings.

Passes all 115 Checkov security checks

Security
Logs and alerts are encrypted with a KMS key that rotates automatically, and CI scans every change.
Built with
TerraformGuardDutySecurity HubAWS ConfigCloudTrailKMS
More details
  • CloudTrail in every region, Security Hub with the AWS best practices and CIS v3.0 standards, and 9 AWS Config rules.
  • Account-wide defaults: S3 public access block, EBS encryption, no public snapshot or AMI sharing, and a strict IAM password policy.
  • Serious GuardDuty and Security Hub findings, and any root user sign-in, send an alert through EventBridge and SNS.
Client work· Private

Single Tenant to Multi-Tenant Migration

Moved each customer's separate deployment onto one shared platform, without interrupting service.

70% lower infrastructure cost

Security
Customers share the platform, but each one's data stays isolated.
Built with
AWSKubernetesTerraformCodeBuildDocker
More details
  • Onboarded 8 tenants with the same provisioning and governance process.
  • The client formally recognized the team for the quality of the delivery.
Client work· Private

Multi-Tenant Microservices on EKS

A Kubernetes platform on Amazon EKS that runs many customers' services side by side.

35+ microservices, 15+ tenants, zero-downtime releases

Security
Kubernetes RBAC controls tenant access, and every deploy goes through Argo CD.
Built with
AWS EKSKubernetesArgo CDHelmPrometheus
More details
  • Workloads scale with the Horizontal Pod Autoscaler.
  • Prometheus and Grafana dashboards catch problems early.
Client work· Private

DevSecOps Pipeline

CI/CD pipelines that build, scan, and deploy applications written in Node.js, Java, .NET, and Python.

40% faster deployments across 8+ apps

Security
Snyk and SonarQube run on every build, and a build fails on critical findings.
Built with
JenkinsGitHub ActionsCodePipelineSnykSonarQube
More details
  • Supported SOC 2 and HIPAA audits with access controls, audit trails, AWS Security Hub, Config, and Inspector.
Client work· Private

Enterprise AI Knowledge Assistant

Cloud infrastructure for an internal AI knowledge assistant running on Amazon Bedrock.

Fully provisioned with Terraform and GitHub Actions

Security
IAM roles follow least privilege, and every infrastructure change goes through Terraform and CI.
Built with
AWS BedrockTerraformGitHub ActionsIAM

04

Credentials

Education

  • Master of Computer Science

    Algoma University, Brampton, ON

    Jan 2025 – Jan 2026

  • B.Tech in Computer Science and Engineering

    Chandigarh Engineering College, Mohali, India

    July 2017 – July 2021

Certifications

Awards

  • DevOps Engineer of the Quarter

    Sourcefuse

    For delivering cloud migrations, infrastructure automation, and operational improvements.

  • Client Recommendation

    Sourcefuse

    For migrating enterprise workloads and improving the efficiency of the client's cloud infrastructure.